A forgotten Open WebUI admin password can block administration. An offline Docker reset with SQLite restores access to the existing local administrator account without deleting the data volume.
The local password belongs to the account's entry in the auth table. A disposable Alpine repair shell can replace that password while the application is stopped. This method requires host access to the existing data volume and does not apply to an external PostgreSQL database or an identity provider's password.
A password reset does not remove multi-factor authentication. An enrolled account still needs its authenticator or recovery code; a lost second factor needs separate MFA recovery. A verified backup remains essential because editing the wrong database or account can leave the administrator locked out.
Steps to reset an Open WebUI admin password in Docker with SQLite:
- Create a verified offline backup using How to back up and restore Open WebUI data.
The backup must include the entire data volume and the original secret configuration, with a successful restore rehearsal. Deleting webui.db removes account records and chat history rather than recovering the existing account.
- Confirm the data volume mounted at /app/backend/data in the application container.
$ docker inspect --format '{{range .Mounts}}{{println .Name .Destination}}{{end}}' open-webui
open-webui /app/backend/data
The commands assume the container and named volume are both open-webui. Different names must match the existing deployment; a bind-mounted data directory needs that same host directory mounted at /data in the repair container.
- Stop the Open WebUI application container.
The service remains unavailable until the container starts again. Every process writing to this data volume must be stopped during the database edit.
$ docker stop open-webui
open-webui
- Open a disposable repair shell with the existing data volume mounted at /data.
$ docker run --rm -it -v open-webui:/data alpine:3.22 sh
/ #
- Install htpasswd and sqlite3 inside the repair shell.
/ # apk add --no-cache apache2-utils sqlite
- Restrict temporary files to the repair-shell user.
/ # umask 077
- Generate the new password hash with hidden interactive entry.
/ # htpasswd -nBC 10 "" > /tmp/admin.hash
New password:
Re-type new password:
The prompts do not display the password. The protected file holds the generated hash inside the disposable container; neither the password nor the hash belongs in a shared transcript.
- Open the existing SQLite database.
An absent webui.db means the wrong volume or path may be mounted. Continuing can create an empty database instead of repairing the existing installation.
/ # sqlite3 /data/webui.db
- Identify the matching administrator account using its lowercase email address.
sqlite> SELECT auth.email, USER.role
   ...> FROM auth JOIN USER ON auth.id = USER.id
   ...> WHERE auth.email = LOWER('Admin@example.com');
admin@example.com|admin
The address represents the locked-out account. Exactly one row with role admin must appear before any update; no row, multiple rows, or a different role requires investigation.
- Begin a database transaction for the password change.
sqlite> BEGIN IMMEDIATE;
- Replace only the identified administrator's password with the generated hash.
sqlite> UPDATE auth
   ...> SET password = rtrim(
   ...>     substr(CAST(readfile('/tmp/admin.hash') AS TEXT), 2),
   ...>     CHAR(10) || CHAR(13))
   ...> WHERE email = LOWER('Admin@example.com')
   ...> AND id IN (SELECT id FROM USER WHERE ROLE = 'admin');
htpasswd prefixes the hash with a colon for the empty username. substr(…, 2) removes that colon, and rtrim removes trailing line-feed and carriage-return characters without printing the hash.
- Check that exactly one password row changed.
sqlite> SELECT changes();
1
If the result is not 1, ROLLBACK; cancels the uncommitted change. A row count alone does not prove that the new password works.
- Commit the one-row password change.
sqlite> COMMIT; - Quit sqlite3.
sqlite> .quit
- Leave the disposable repair shell.
/ # exit
The docker run –rm container and its temporary hash file are removed; the mounted data volume remains.
- Start the Open WebUI application container again.
$ docker start open-webui
open-webui
Startup may take several minutes. An application error belongs in How to view Open WebUI Docker logs before another database edit.
- Open the instance's sign-in page in a private browser window.
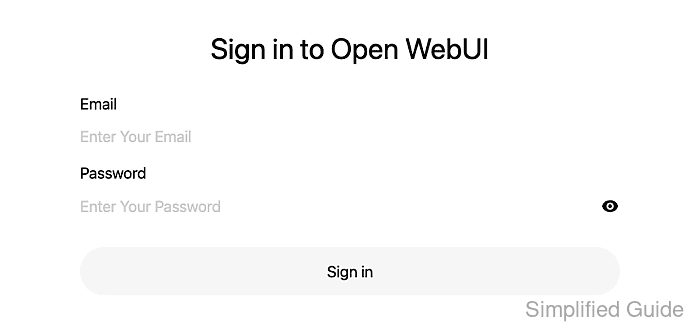
- Enter the administrator's email address in Email.
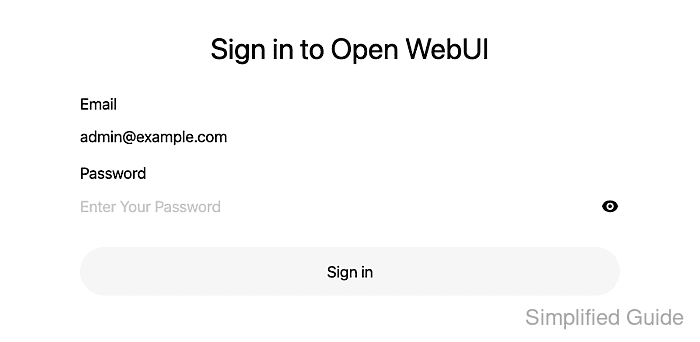
- Enter the new password in Password.
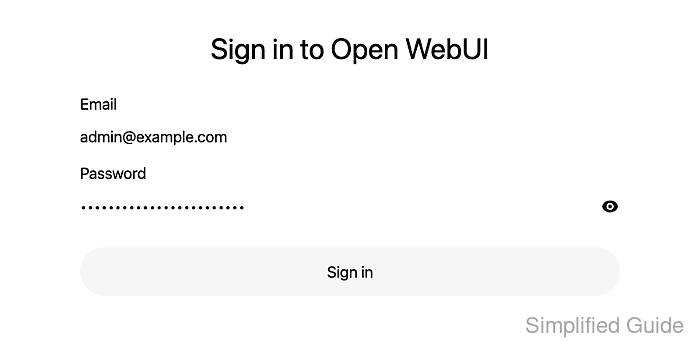
- Click Sign in.
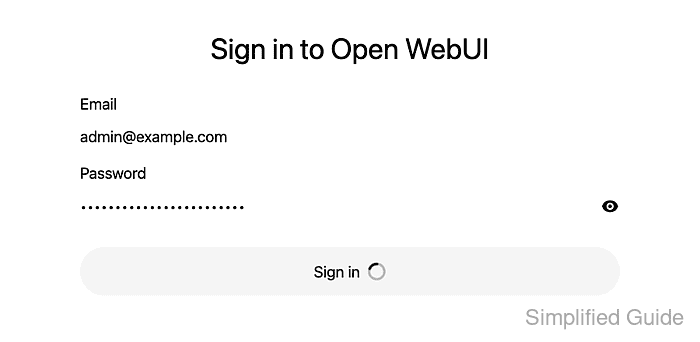
If MFA is enabled, the existing authenticator or an unused recovery code is still required.
- Dismiss the first-visit release notes if they cover the workspace.
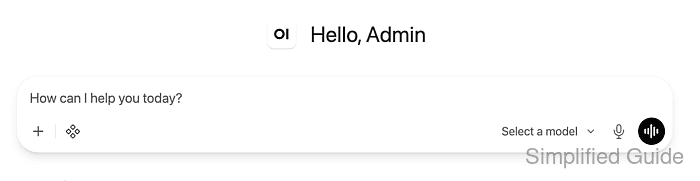
- Confirm that the account reaches the chat workspace.
- Open the account menu.
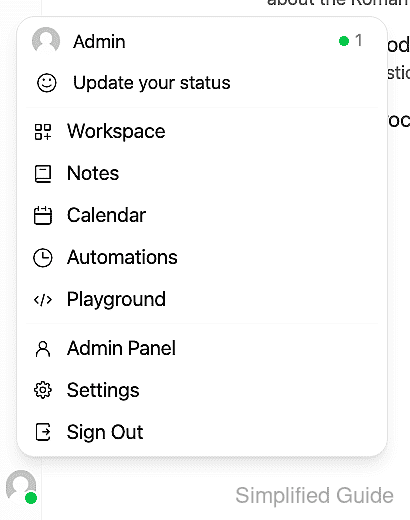
- Select Admin Panel.
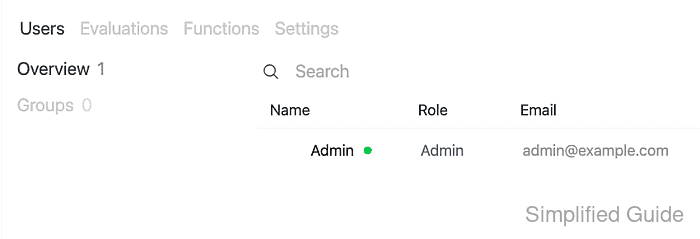
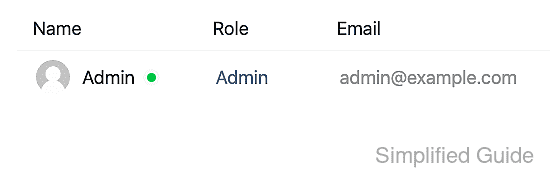
- Confirm that the Users page lists the recovered account with the Admin role.
The new password now opens an authenticated administrator session. The verified backup remains the recovery point if other problems appear.