Open WebUI keeps chats, users, settings, and uploaded files outside the disposable container image. A volume backup provides a recovery point before an update or storage change, and a restore rehearsal checks whether those records and files are usable again.
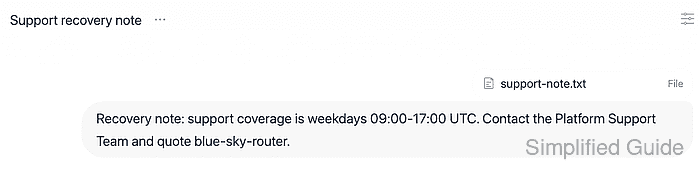
The standard Docker deployment stores its local SQLite database, uploads, and vector data in the open-webui volume. An offline archive of the whole volume preserves these together. External databases, object storage, and external vector stores need their own backups and are outside this volume-only method.
A restore rehearsal needs an existing account, a recognizable conversation, and an uploaded file whose original copy is still available. The original image and a protected env file containing the active WEBUI_SECRET_KEY are prerequisites. Docker's default generated key sits outside the data volume, so the archive alone does not preserve it.
Steps to back up and restore Open WebUI data:
- Record the SHA-256 hash of a local file already attached to a saved conversation.
$ shasum -a 256 support-note.txt
338235ea10a1cce8988b65e25fb751d1405822d553bf9605af43c5f18231719b  support-note.txt
support-note.txt represents the original copy of your chosen upload. A recognizable message in that same conversation supplies a separate check of the restored database.
- Confirm the named volume mounted at /app/backend/data in the source container.
$ docker inspect --format '{{range .Mounts}}{{println .Name .Destination}}{{end}}' open-webui
open-webui /app/backend/data
The remaining commands assume that both the container and volume are named open-webui. A Compose stack may use a project-prefixed volume name.
- Retain the source image ID for the restore container.
$ image=$(docker inspect --format '{{.Image}}' open-webui)
Starting with the same image avoids introducing database migrations during recovery.
- Restrict new backup files to the current user.
$ umask 077
The backup contains private conversations, uploads, password hashes, and potentially integration credentials. The restricted directory and file modes limit access to trusted operators.
- Create a new host directory for the backup.
$ mkdir -m 700 open-webui-backups
- Copy the existing protected env file into the backup directory.
$ cp open-webui.env open-webui-backups/open-webui.env
This assumes open-webui.env contains the original WEBUI_SECRET_KEY, as in How to run Open WebUI with Docker. An installation without its original key already retained is not ready for this rehearsal. Generating a replacement key can invalidate sessions and prevent decryption of stored credentials.
- Assign a dated filename to the archive.
$ archive="openwebui-$(date +%Y%m%d-%H%M%S).tar.gz"
- Stop the source Open WebUI container.
The service is unavailable until it is started again. Every other process writing to this volume must also be stopped before the archive is taken.
$ docker stop open-webui
open-webui
- Archive the stopped instance's entire data volume.
$ docker run --rm --mount type=volume,src=open-webui,dst=/data,readonly alpine:3.22 tar -czf - -C /data . > "open-webui-backups/$archive"
The source mount is read-only. Tar runs as root to read every volume file, while your host shell creates the archive with your ownership and mode 600 under the earlier umask 077. Archiving the entire directory includes hidden entries and any remaining SQLite WAL files, rather than copying webui.db alone. If archiving fails, the original container can be restarted while the backup failure is investigated.
- Start the original container after the archive command succeeds.
$ docker start open-webui
open-webui
- Restrict access to the completed archive.
$ chmod 600 "open-webui-backups/$archive"
- Check the archive for the database and uploaded files.
$ tar -tzf "open-webui-backups/$archive"
./
##### snipped #####
./webui.db
##### snipped #####
./uploads/
##### snipped #####
The listing must contain ./webui.db and the uploaded-file paths used by the instance. Vector-store paths appear when local indexing has been used. An empty archive or a failed listing is not a usable recovery point.
- Create a fresh volume for the restore rehearsal.
The target must be empty. A volume with this name may already exist from an earlier rehearsal; the extraction command refuses a nonempty target instead of deleting its contents.
$ docker volume create open-webui-restore-test
open-webui-restore-test
- Extract the archive into the empty restore volume.
$ docker run --rm --mount type=volume,src=open-webui-restore-test,dst=/data --mount type=bind,src="$PWD/open-webui-backups",dst=/backup,readonly alpine:3.22 sh -c 'test -z "$(ls -A /data)" && tar -xzf "/backup/$1" -C /data' sh "$archive"
A nonzero exit status requires investigation before starting the restored app. The source volume and archive are unchanged.
- Start the restored instance on a host-only port with the original image and env file.
This creates a second copy of the instance's private data. The loopback listener limits browser access, but it does not block outbound integration traffic. A rehearsal with active automations or external integrations belongs on an isolated recovery host. Docker Engine 28.0.0 or newer is required for this loopback network boundary.
$ docker run -d --name open-webui-restore-test -p 127.0.0.1:3001:8080 -v open-webui-restore-test:/app/backend/data --env-file open-webui-backups/open-webui.env "$image"
- Check that the restored application is ready.
$ curl -fsS http://127.0.0.1:3001/health
{"status":true}
Startup can take several minutes. Health confirms readiness; the account, chat, and file checks below establish recovery.
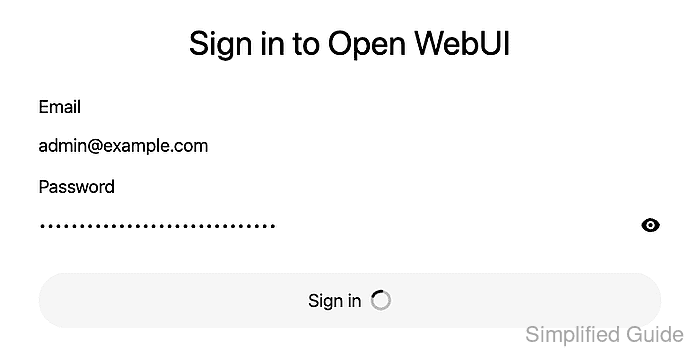
- Open http://127.0.0.1:3001 in a separate private browser window.
- Enter the email address of an existing account in Email.
- Enter that account's password in Password.
- Click Sign in.
- Confirm that the restored account reaches its chat workspace.
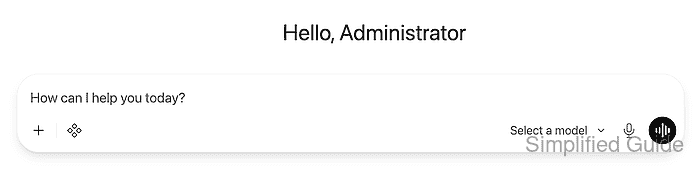
First-visit release notes can cover the workspace until dismissed.
- Open the chat sidebar.
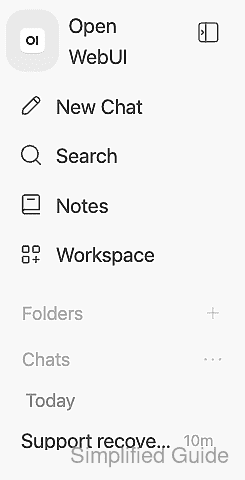
- Open the known conversation from chat history.
The title and saved message text must match the source conversation. A successful login alone does not prove chat recovery.
- Open the uploaded file attached to the restored conversation.
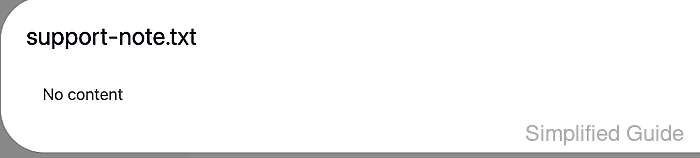
The preview uses extracted text. No content can appear for an upload that was never processed; it does not establish whether the original uploaded bytes are available.
- Open the original file using its filename link in the preview.
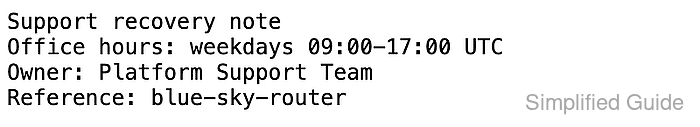
- Download the original file by appending ?attachment=true to its address.
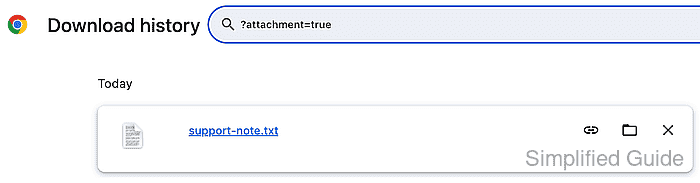
The browser's download history shows the completed file under its original filename.
- Compare the downloaded file's hash with the original file's hash.
$ shasum -a 256 support-note.txt ~/Downloads/support-note.txt
338235ea10a1cce8988b65e25fb751d1405822d553bf9605af43c5f18231719b  support-note.txt
338235ea10a1cce8988b65e25fb751d1405822d553bf9605af43c5f18231719b  /Users/user/Downloads/support-note.txt
The two hashes must match. The actual download path follows the browser's settings. The archive, matching secret configuration, and original instance remain the recovery resources.
- Remove the disposable restore container after the rehearsal.
$ docker rm -f open-webui-restore-test
open-webui-restore-test
- Remove the rehearsal volume containing the copied private data.
$ docker volume rm open-webui-restore-test
open-webui-restore-test
The original open-webui volume and protected backup directory remain available.