AWS S3 buckets are set to private by default. This ensures that objects within the bucket are inaccessible to unauthorized users. However, in some cases, you might need to make certain objects or entire buckets publicly accessible.
To allow public access, you can either enable public access for the entire bucket or for specific objects. Granting public access at the bucket level involves configuring the appropriate public access policy. If you prefer a more controlled approach, public access can be granted to individual objects.
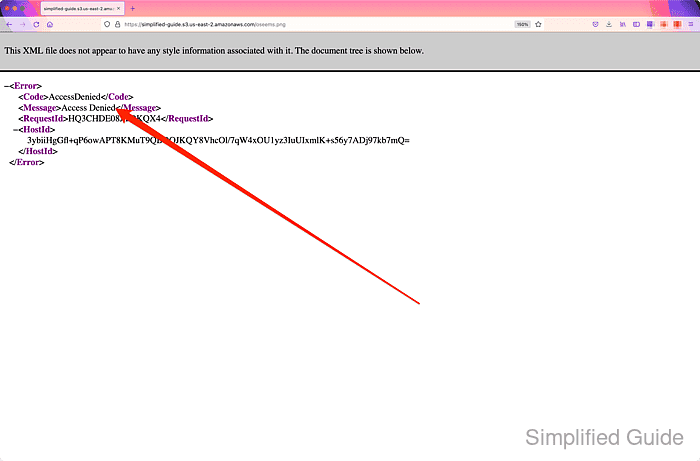
Making an object public takes a change to the bucket and a change to the object. Turning off Block public access publishes nothing by itself, but it removes the bucket's guard against public ACLs and public bucket policies for every object in it, so keep sensitive files in a different bucket. The object's URL returns Access Denied until its ACL allows public read access, then opens for anyone who has the link.
Steps to allow public access to private AWS S3 bucket objects:
- Create a private S3 bucket if you don't already have one.
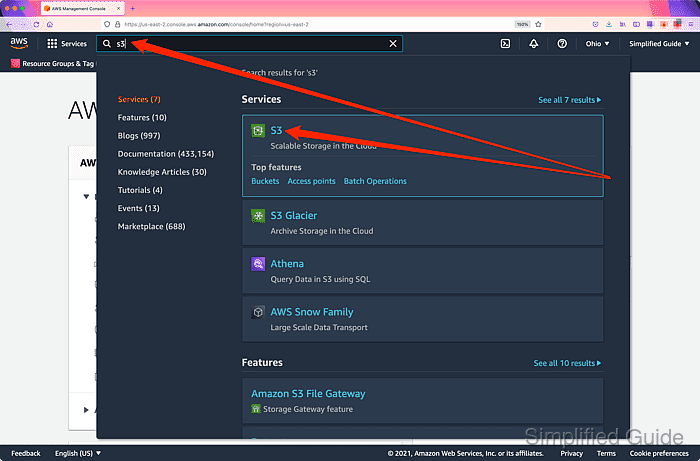
- Go to S3 section in your AWS Console.
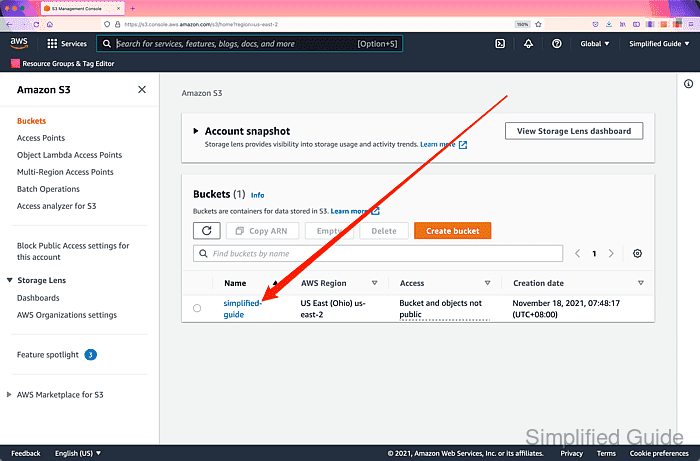
- Click on the private S3 bucket with the object that you want to make public.
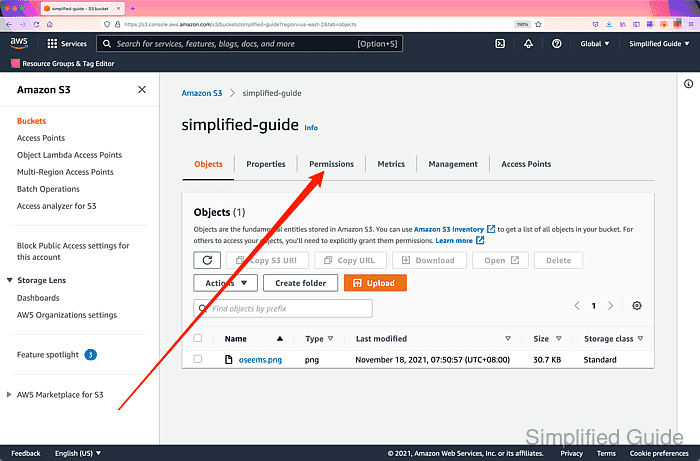
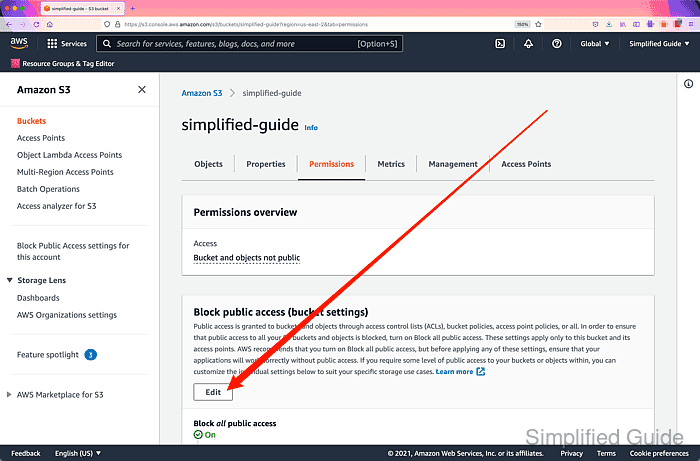
- Click on the Permissions tab.
- Click Edit on the Block public access section.
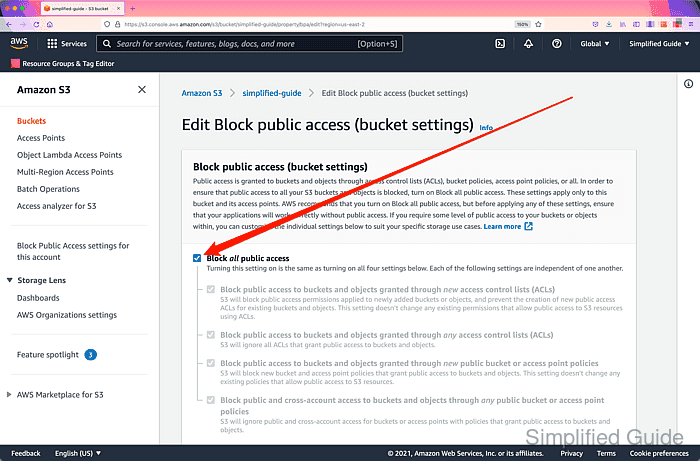
- Click on the Block all public access to uncheck and disable the options.
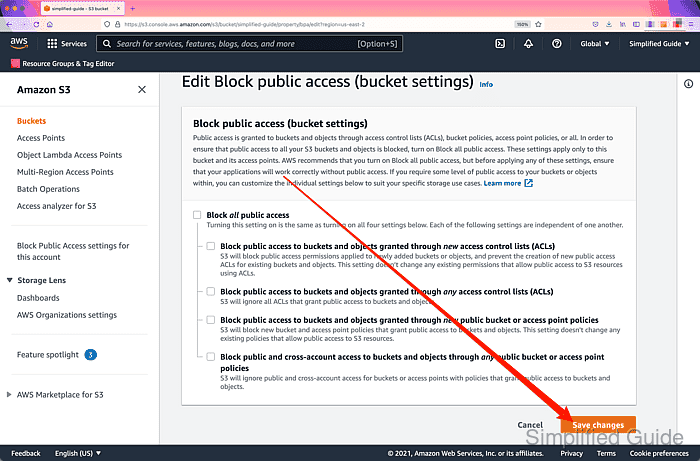
- Click on the Save changes button.
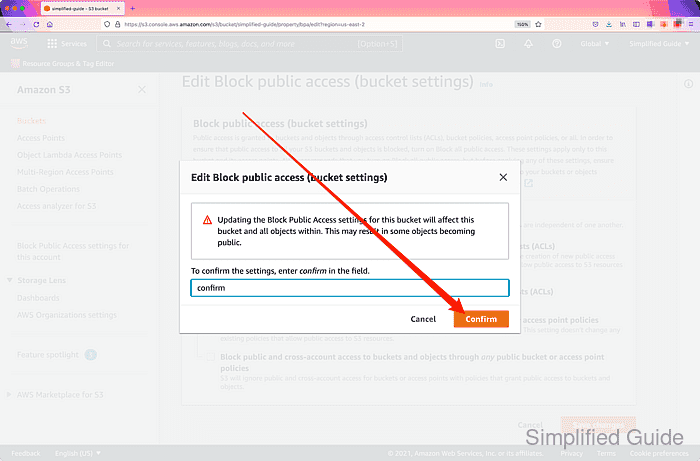
- Type confirm in the textbox to confirm.
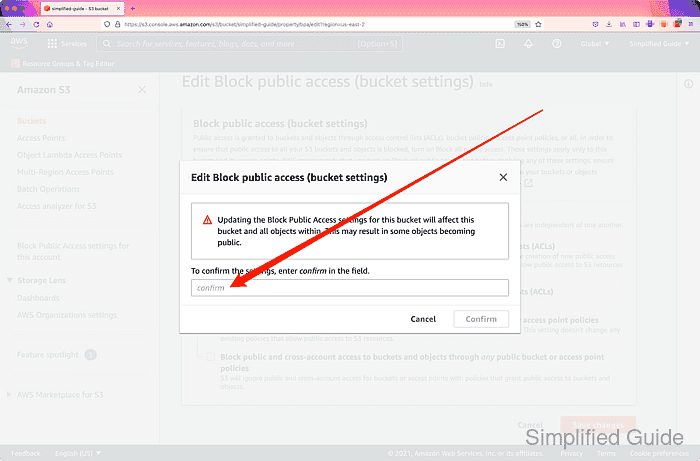
- Click on the Confirm button.
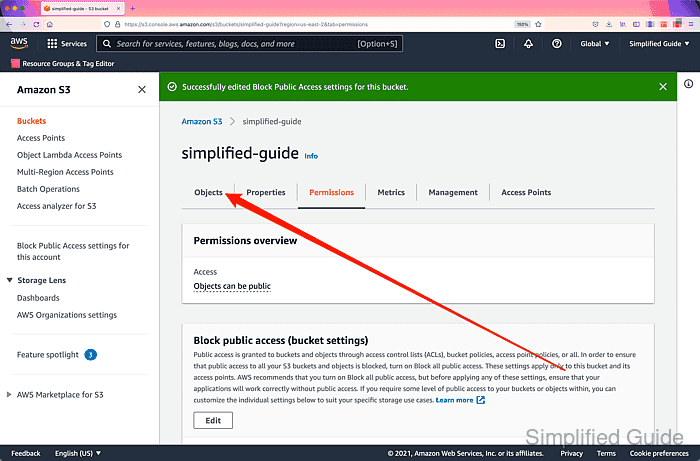
- Click on the Objects tab.
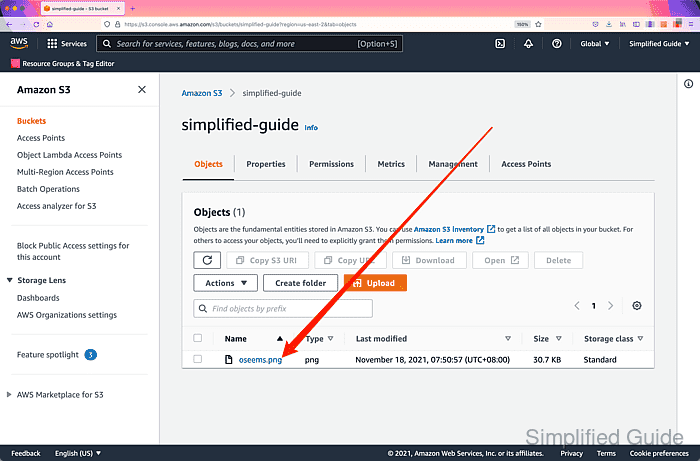
- Click on the object that you want to make public.
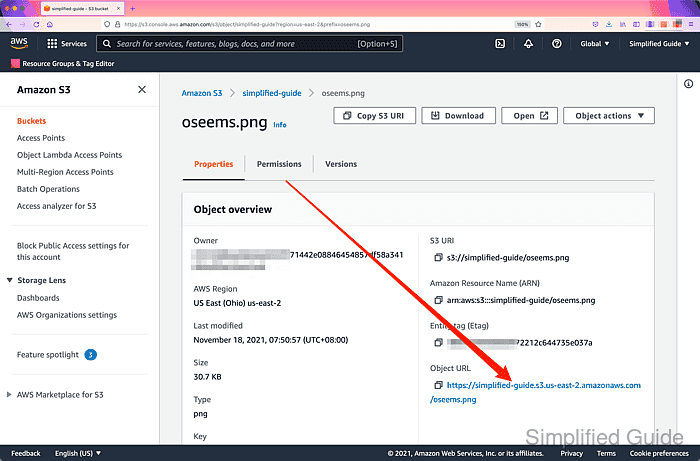
- Click on the Object URL link to test current object access.
- Confirm current object access is still private and go back to object's properties page.
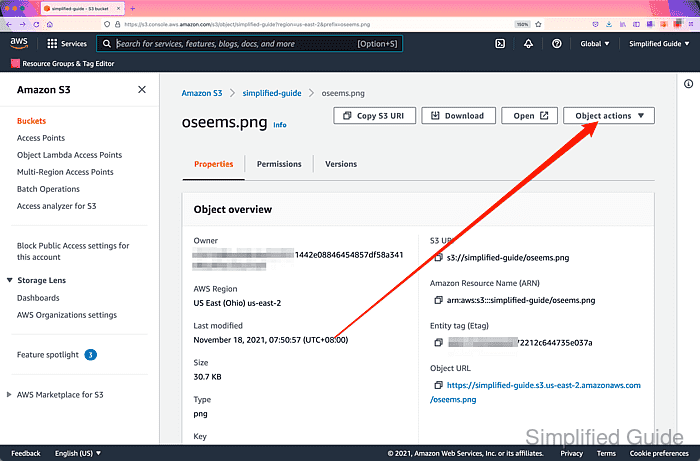
- Click on the Object actions dropdown menu.
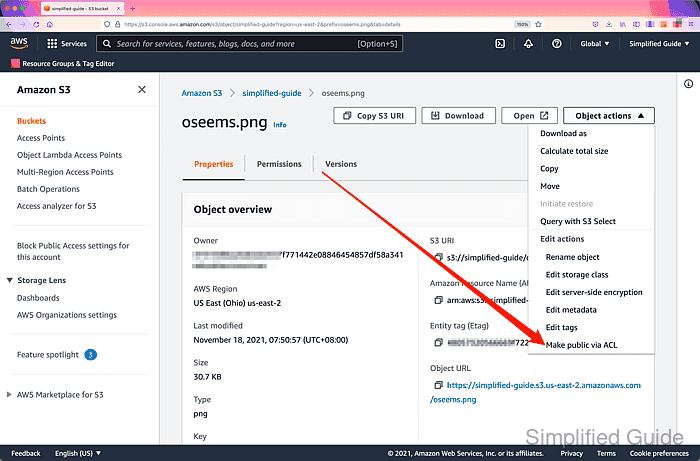
- Click on Make public via ACL.
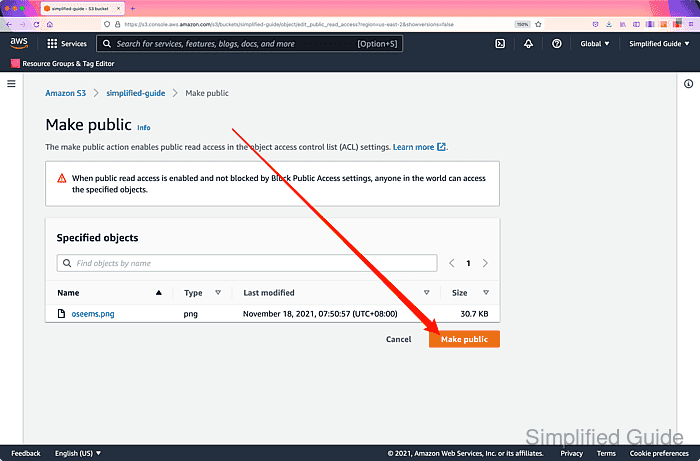
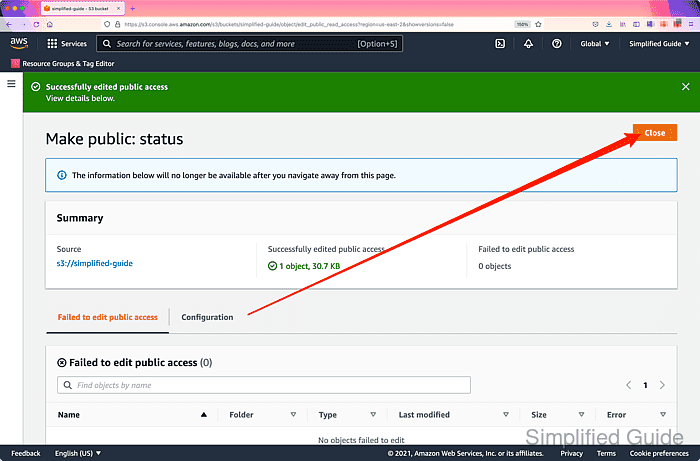
- Click on the Make public button.
- Click on the Close button.
- Click on the link in the Object URL again to test.
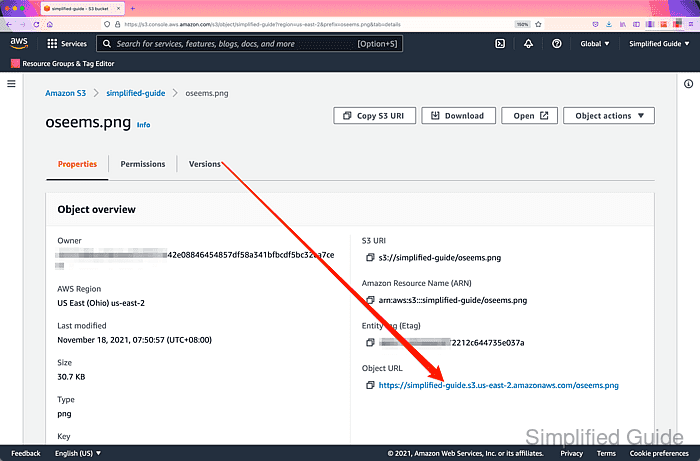
- Confirm current object access is now public.