S3 buckets are private by default to protect data from unintended access. To make an S3 bucket public, you must modify its permissions and configure the appropriate Bucket policy. This is necessary if you want to share files or host content, such as a static website, publicly.
S3 Block Public Access overrides any Bucket policy or access control list that allows public access. The same setting can also apply to a whole AWS account or organization, and the most restrictive setting wins, so a block at either level still applies after the bucket's own setting is turned off.
After enabling public access, it’s essential to define a clear Bucket policy to control what can be accessed. This policy determines which objects within the bucket are publicly accessible and specifies the actions allowed. Properly configuring this ensures that only intended content is available to the public, while other data remains secure.
Steps to create public AWS S3 bucket:
- Create a private S3 bucket if you don't already have one.
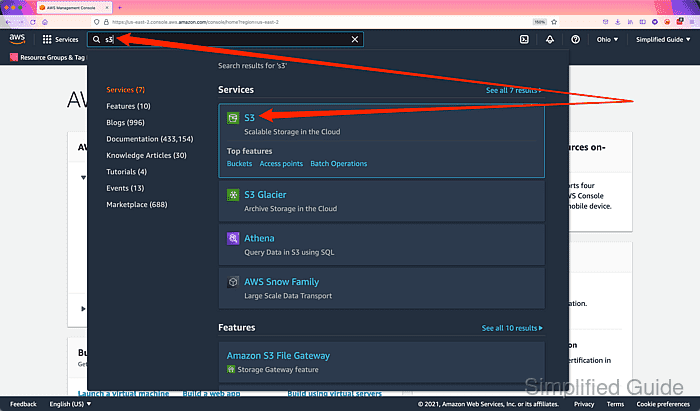
- Go to S3 section in your AWS Console.
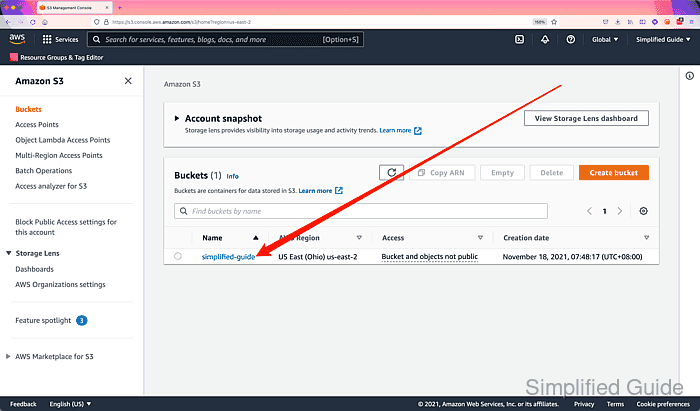
- Click on the private S3 bucket that you want to make public.
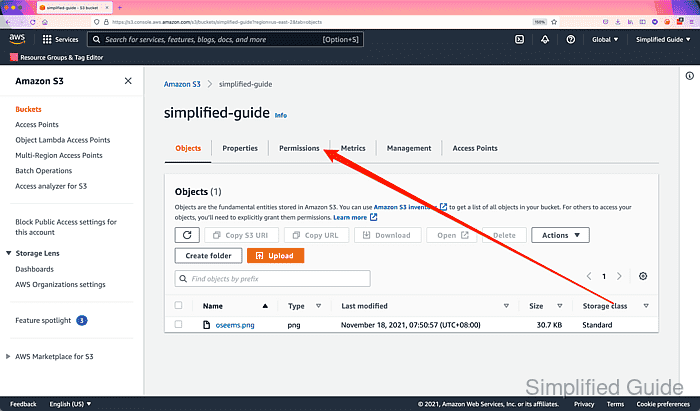
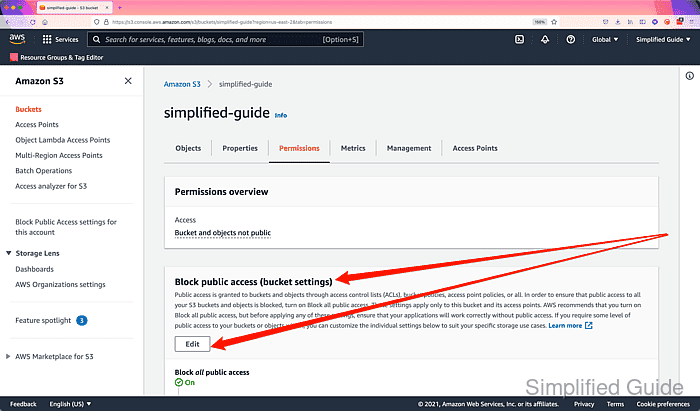
- Click on the Permissions tab of your S3 bucket.
- Go to Block public access section and click on Edit.
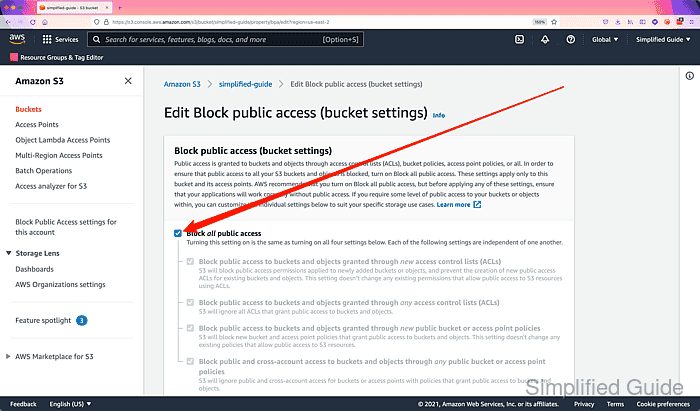
- Click to uncheck the Block all public access checkbox.
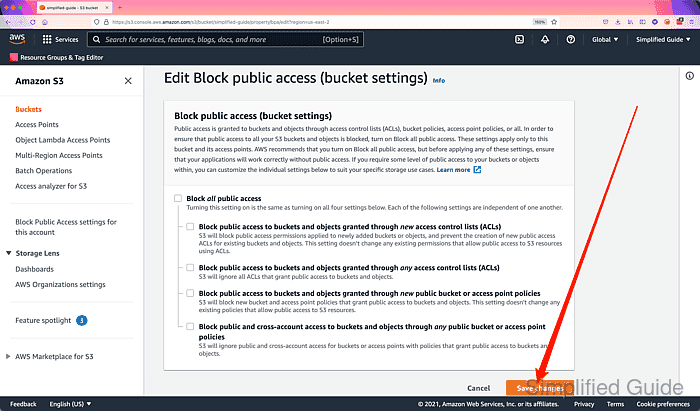
- Click on the Save changes button.
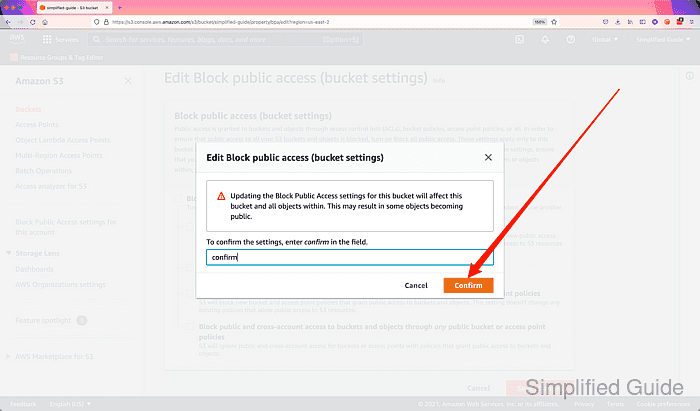
- Type confirm in the textbox to confirm your action.
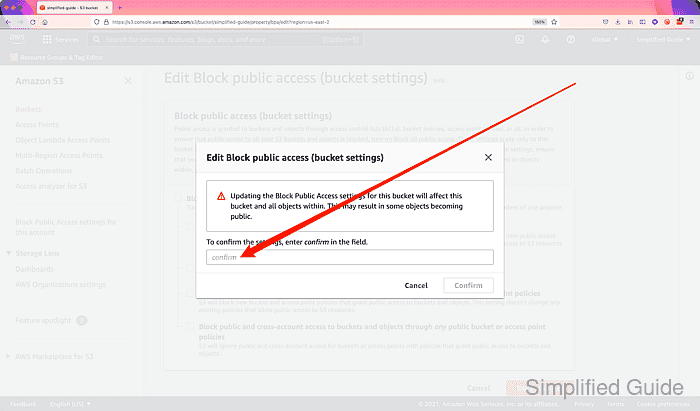
- Click on the Confirm button.
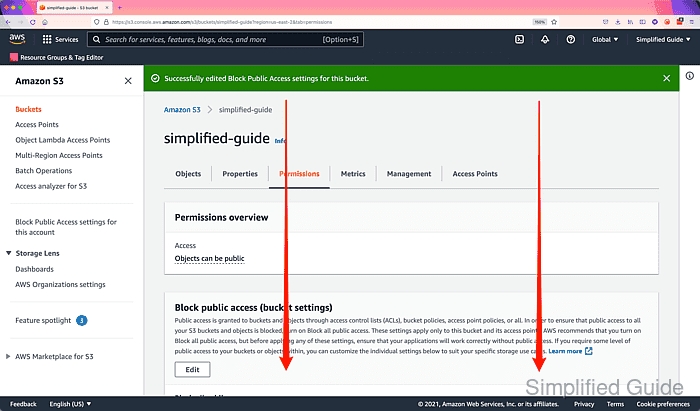
- Scroll down to the Bucket policy section.
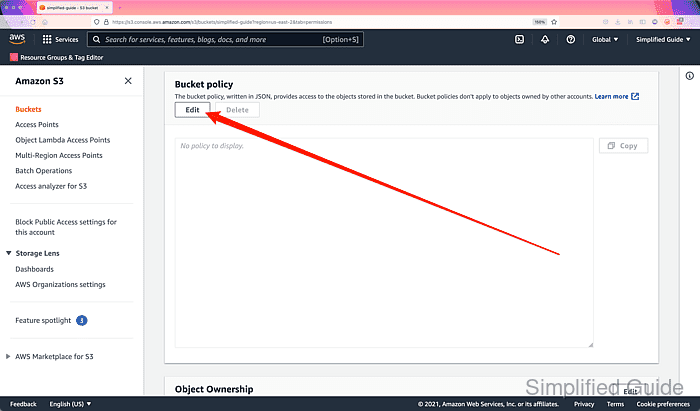
- Click on the Edit button.
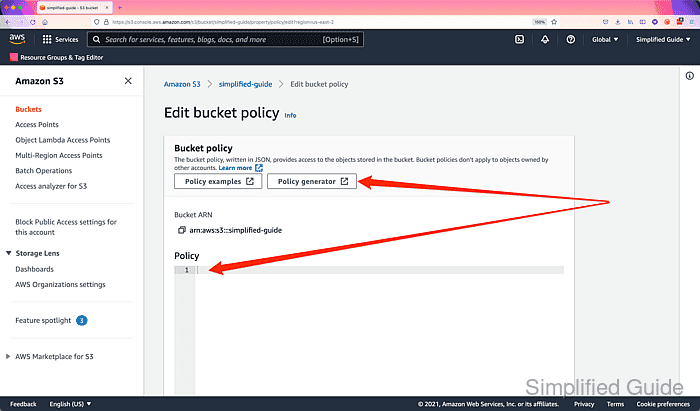
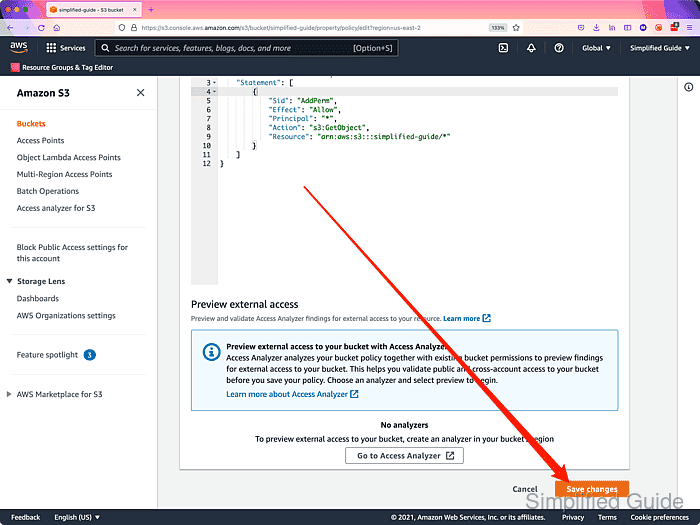
- Enter and review the policy to make your S3 bucket public or use the Policy generator.
{
  "Version":"2012-10-17",
  "Statement":[
    {
      "Sid":"AddPerm",
      "Effect":"Allow",
      "Principal": "*",
      "Action":["s3:GetObject"],
      "Resource":["arn:aws:s3:::simplified-guide/*"]
    }
  ]
}
Replace simplified-guide with your own bucket name.
- Click on the Save changes button.
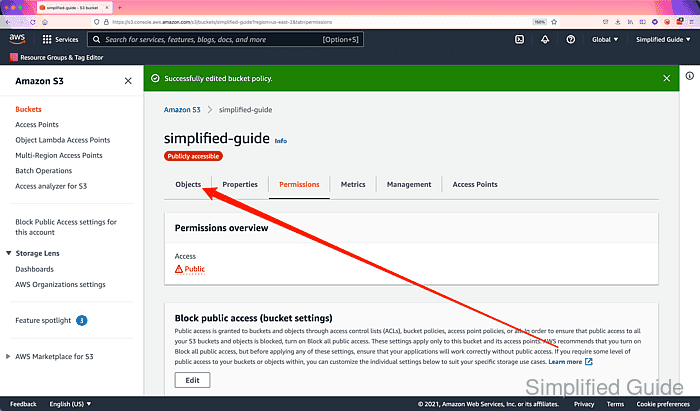
- Go to the Objects tab.
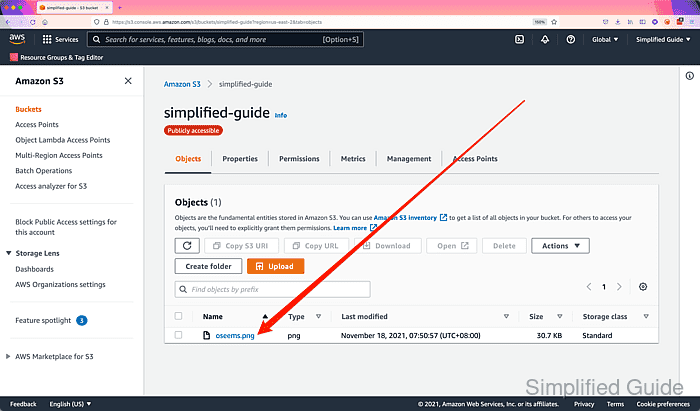
- Click on an object.
- Click on the link on the Object URL section.
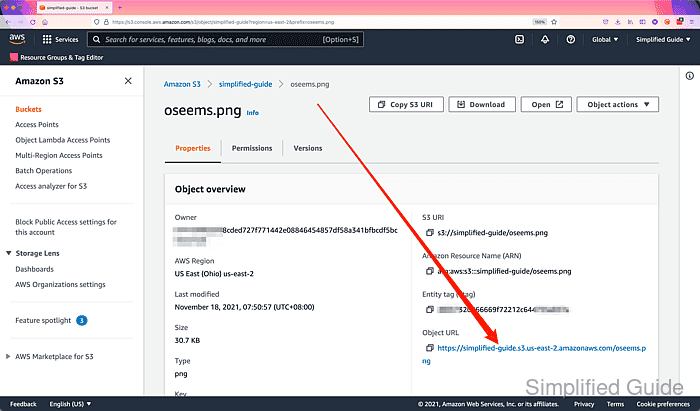
- View the object using the publicly accessible URL.