Resetting a WordPress user password with WP-CLI restores access when the dashboard reset email, an administrator session, or a hosting control panel is not available. The wp user reset-password command changes one account from the shell and can print a generated temporary password for a controlled handoff.
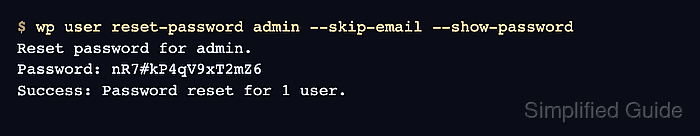
WP-CLI loads the WordPress install from the document root or --path value, then writes the password change to the connected database. On multisite, --url keeps the command in the intended site context, and the user argument can be a login, email address, or numeric ID.
The printed password is an emergency credential, not a permanent shared secret. Confirm the target account first, give the temporary value through a private channel, and have the user replace it after login or rotate it again from the shell.
Steps to reset a WordPress user password with WP-CLI:
- Change into the exact WordPress document root.
$ cd /var/www/example.com/public_html
In automation or shared shell sessions, add --path=/var/www/example.com/public_html to each wp command instead of relying on the inherited working directory.
Related: How to use WP-CLI safely on a production WordPress site - Confirm that WP-CLI is targeting the intended site.
$ wp option get home
https://www.example.com
On multisite, add --url=https://www.example.com to the remaining site-specific commands.
- List users and identify the account to reset.
$ wp user list --fields=ID,user_login,user_email,roles
ID	user_login	user_email	roles
1	admin	admin@example.com	administrator
Reset the login, email address, or ID that belongs to the affected account. A password reset for the wrong administrator can create a second access incident.
- Reset the target user's password and print the generated temporary value.
$ wp user reset-password admin --skip-email --show-password
Reset password for admin.
Password: nR7#kP4qV9xT2mZ6
Success: Password reset for 1 user.
The printed password can grant immediate access to wp-admin. Keep the terminal private, do not paste the real value into tickets or chat, and remove --skip-email only when the site's mailer is trusted and the user should receive a password-change email.
- Verify that WordPress accepts the temporary password.
$ wp user check-password admin 'nR7#kP4qV9xT2mZ6' && echo "Password accepted"
Password accepted
wp user check-password is silent on success; the echo text only makes the zero exit status visible. Use a private shell if the real password could be recorded in shared history or session logs.
- Confirm the account identity and role after the reset.
$ wp user get admin --fields=ID,user_login,user_email,roles --format=table
Field	Value
ID	1
user_login	admin
user_email	admin@example.com
roles	administrator
- Give the temporary password to the account owner through a private channel.
Have the user replace the temporary password after login. If the account was reset only for emergency administrator access, rotate it again before closing the incident.