Linux sign-in failures can come from separate account controls. Access to a local user account is restored by identifying its lock, clearing only that block, and retesting the original login path.
On shadow-managed Linux systems, a password lock and account expiry are independent restrictions. A pam_faillock tally can also reject a correct password after repeated failed logins, so a usable password alone does not prove that sign-in will work.
Restoring access must be authorized, and a separate working administrator session provides recovery if sign-in still fails. Local account repairs do not unlock identities managed by LDAP, Active Directory, or an upstream identity service, and legitimate account-expiry or password-age policies should remain in force.
Steps to unlock a local user account in Linux:
- Check whether the account password is locked.
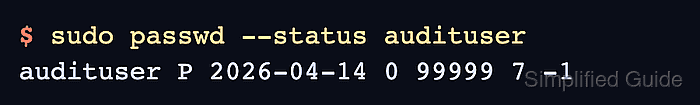
$ sudo passwd --status audituser
audituser L 2026-11-06 0 99999 7 -1
audituser represents the affected login name, and an account with sudo access is required. The second field shows L or LK for locked, P or PS for a usable password, or NP for no password, depending on the distribution.
- Check whether the account has expired.
$ sudo chage --list audituser
Last password change					: Nov 06, 2026
Password expires					: never
Password inactive					: never
Account expires						: Jan 02, 1970
Minimum number of days between password change		: 0
Maximum number of days between password change		: 99999
Number of days of warning before password expires	: 7
A past Account expires date blocks sign-in even when the password works. An expired or forgotten password needs a password change instead.
Related: How to change a user password in Linux - Check the failed-login tally if the login service uses pam_faillock.
$ sudo faillock --user audituser
audituser:
When                Type  Source                                           Valid
2026-11-06 15:24:37 RHOST 127.0.0.1                                            V
2026-11-06 15:24:40 RHOST 127.0.0.1                                            V
2026-11-06 15:24:43 RHOST 127.0.0.1                                            V
Failures marked V count toward the lockout, but the block only applies once they reach the service's limit and until its unlock timer runs out.
Related: How to lock accounts after failed login attempts in Linux - Unlock the password only if its status is L or LK.
This brings back the previous password without changing it. If the unlock is refused or the old password is no longer trusted, set a new password instead.
Related: How to change a user password in Linux$ sudo passwd --unlock audituser passwd: password changed.
- Clear a past account-expiry date only if it was an administrative hold and no fixed expiry is required.
This removes the account's end date. A required future expiry must stay in place. To renew an expired account until a fixed end date, use the approved YYYY-MM-DD date in place of -1.
$ sudo usermod --expiredate -1 audituser
- Reset this user's failed-login tally if it is blocking sign-in.
This clears the failure records for this account only and leaves the lockout policy in place.
$ sudo faillock --user audituser --reset
- Have the account's user sign in the same way that failed.
$ ssh audituser@server.example.net
audituser@server.example.net's password:
##### snipped #####
Last login: Fri Nov  6 15:24:36 2026 from 127.0.0.1
audituser@server:~$
server.example.net stands for the affected host. The account's user types their own password and never gives it to the administrator, and a shell prompt shows the sign-in worked. For a console or desktop lockout, sign in there instead. If sign-in still fails, the cause may be a mistyped password, which also adds to any failed-login tally, or something outside these locks, such as a nologin shell or an SSH access rule.