Protected HTTPS downloads may require Basic authentication. Wget can fetch these resources with a username and a prompted password, keeping the password out of the command text.
On a normal Basic-auth exchange, Wget requests the URL, receives a 401 Unauthorized response with a WWW-Authenticate: Basic challenge, and retries with an Authorization header when credentials are available. This authenticates an HTTP request; a browser login form may require cookies or a different login method.
Basic auth should stay on trusted HTTPS endpoints because the scheme itself does not protect the password without transport encryption. Literal passwords in command arguments or URLs can leak through process listings, shell history, and logs. Prompted entry is for interactive use; unattended jobs need a separately configured, protected credential source because a scheduler cannot answer a terminal password prompt.
Steps to use a username and password with Wget:
- Fetch the protected HTTPS resource with your username and a prompted password.
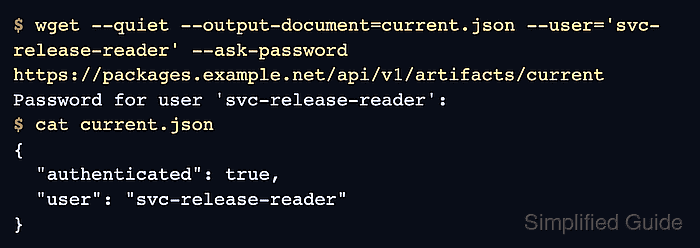
The account and URL below stand for your own authorized download. --user supplies the username, and --ask-password reads the password without displaying it. --ask-password and --password cannot be used together.
--output-document=current.json replaces any existing current.json immediately, even if the request later fails.
$ wget --quiet --output-document=current.json --user='svc-release-reader' --ask-password https://packages.example.net/api/v1/artifacts/current
Password for user 'svc-release-reader':
--quiet hides transfer messages, so silence after the prompt does not prove that authentication succeeded.
- Inspect the response headers if the authenticated download fails.
$ wget --server-response --output-document=current.json --user='svc-release-reader' --ask-password https://packages.example.net/api/v1/artifacts/current
An initial 401 Unauthorized with WWW-Authenticate: Basic followed by 200 OK is the normal exchange. A final 401 after the credential retry means the server rejected the credentials for that resource or realm. A 401 without a Basic challenge means Wget has no Basic challenge to answer; it does not establish that the password is wrong. A 403 Forbidden means the server refuses access and can indicate insufficient account permissions or another server policy, even with valid credentials.
- Retry with --auth-no-challenge only when the server's documentation or administrator confirms that it requires preemptive Basic authentication.
This option sends credentials on the first request instead of waiting for a challenge, so it belongs only on the trusted HTTPS endpoint that requires it. It does not fix rejected credentials or grant missing permissions.
$ wget --quiet --output-document=current.json --auth-no-challenge --user='svc-release-reader' --ask-password https://legacy-gateway.example.net/session/health
Password for user 'svc-release-reader':
- Confirm that the saved response contains the protected content expected for your account.
$ cat current.json
{
  "authenticated": true,
  "user": "svc-release-reader"
}
The response format depends on the endpoint. Here, authenticated and user confirm access as the intended account. An empty file, a login page, or an error document does not prove access, even if a server returned 200 OK.