AppArmor limits what a program can access even when its Linux account has permission. Disabling AppArmor removes those profile restrictions, so an application blocked by a profile can run unconfined. When only one application is affected, try disabling that profile first to keep other applications confined.
System-wide disabling also removes AppArmor protection from services and containers that use it. Strict snaps rely on AppArmor, Docker uses the docker-default container profile, and LXD uses AppArmor as part of container isolation. Ubuntu's AppArmor restriction on unprivileged user namespaces also depends on AppArmor staying enabled. Ordinary file permissions and other security mechanisms remain, but they do not replace the removed restrictions.
On Ubuntu 24.04, Ubuntu 26.04, and Debian 13, the AppArmor service loads policy into the kernel. Stopping that service does not unload its profiles. A GRUB kernel option disables AppArmor across reboots while leaving the packages and profile files available for recovery; this method requires a machine that boots through GRUB and an account with sudo access.
Steps to disable AppArmor in Ubuntu and Debian:
- Arrange working console access before changing GRUB.
A failed boot on a remote server also removes SSH access. A hypervisor or provider console, or physical access, is needed to repair the boot entry. A system snapshot gives you another recovery option. Disabling AppArmor affects every application confined by it; snap applications can lose confinement or fail, and Docker and LXD containers lose an isolation layer.
- Record the currently loaded AppArmor profiles.
$ sudo aa-status
- Create
/etc/default/grub.dif it does not exist.$ sudo mkdir -p /etc/default/grub.d
- Open
/etc/default/grub.d/99-disable-apparmor.cfgin your text editor.$ sudoedit /etc/default/grub.d/99-disable-apparmor.cfg
- Add the following line at the end of
99-disable-apparmor.cfg.GRUB_CMDLINE_LINUX="$GRUB_CMDLINE_LINUX apparmor=0"
The file is normally new. If it already exists, preserve its other settings and add this line only once. The variable expansion preserves existing kernel arguments. A system using another bootloader needs its own kernel-command-line configuration.
- Save
99-disable-apparmor.cfgin your editor. - Regenerate the GRUB boot configuration.
$ sudo update-grub
Do not reboot if this reports an error. If regeneration fails, the added line needs removing before the boot configuration can be repaired.
- Reboot the system into the updated boot entry.
$ sudo reboot
- Check whether AppArmor is enabled after the reboot.
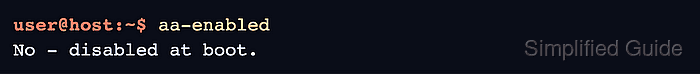
$ aa-enabled
No - disabled at boot.
- Check the kernel's AppArmor enable parameter.
$ cat /sys/module/apparmor/parameters/enabled
N
- Confirm that the kernel is no longer enforcing AppArmor policy.
$ sudo aa-status
apparmor module is loaded.
apparmor filesystem is not mounted.
aa-enabledmust reportNoand the kernel parameter must reportN. The nonzero exit status fromaa-enabledis expected when disabled.aa-statusmay still say the AppArmor module is loaded, followed by a message that its filesystem is not mounted; that first line alone does not mean confinement is active. The formerly blocked operation should now succeed unless another permission or security mechanism also blocks it.
Why service commands do not fully disable AppArmor
sudo systemctl stop apparmorleaves loaded profiles enforcing because the service stop action is a no-op.sudo aa-teardownattempts to unload profiles for the current session. On Ubuntu 24.04 it reported I/O errors and left profiles in unconfined mode after removing enforced and complain profiles. The kernel stays enabled and profiles can be loaded again. Theapparmorpackage provides it.sudo systemctl disable apparmorchanges service startup, without unloading current profiles or disabling the kernel. On Ubuntu,snapd.apparmor.servicecan still load snap profiles after a reboot.
Removing the apparmor package is unnecessary for either method. An APT removal simulation on Ubuntu also selected snapd for removal. On Ubuntu, unloading profiles leaves the restriction on unprivileged user namespaces active. Its sysctl still reports this value.
kernel.apparmor_restrict_unprivileged_userns = 1
With apparmor=0, that sysctl entry is absent and AppArmor no longer restricts unprivileged user namespaces.
Steps to disable one AppArmor profile:
This path starts with AppArmor enabled and changes one local profile under /etc/apparmor.d/. The example values identify a service named report-reader and its existing profile; substitute your application's profile file and service name. A snap or container profile managed by its runtime needs that runtime's controls instead. Restarting the selected service interrupts its current work and connections.
- Identify the application profile in the loaded profile list.
$ sudo aa-status
The profile name shown here can differ from its filename. Other profiles should remain in enforce mode throughout this path.
- Set the profile file and service name for the affected application.
profile=/etc/apparmor.d/usr.local.bin.report-reader
service=report-reader
- Check the running application's confinement label.
$ sudo cat "/proc/$(systemctl show --property MainPID --value "$service")/attr/current"
The service must be running and its PID must be greater than zero. A label ending in
(enforce)confirms enforced confinement for that process. For a desktop application, its actual process ID can be used instead. - List the profile names declared by the selected file.
$ sudo apparmor_parser -N "$profile"
Disabling a file unloads every profile defined in it, including child profiles. All affected processes lose those restrictions. If the file declares unrelated profiles, a file-wide disable is too broad for a one-application test.
- Create the directory used to mark disabled profiles.
$ sudo mkdir -p /etc/apparmor.d/disable
- Prevent the selected profile file from loading at startup.
$ sudo ln -s "$profile" /etc/apparmor.d/disable/
- Unload the selected profile from the running kernel.
$ sudo apparmor_parser -R "$profile"
This works with the base
apparmorpackage. Ifaa-disableis installed,sudo aa-disable “$profile”replaces the directory, link, and unload actions. Theapparmor-utilspackage providesaa-disableon all three releases. - Restart the affected application service.
$ sudo systemctl restart "$service"
For a desktop application, fully quitting and reopening it performs the corresponding restart. A unit with an explicit
AppArmorProfile=setting can fail when its named profile is absent; it needs a service-specific configuration change instead of assuming this path succeeded. - Confirm that the restarted application is unconfined.
$ sudo cat "/proc/$(systemctl show --property MainPID --value "$service")/attr/current"
- Check the target and unrelated profiles in the loaded list.
$ sudo aa-status
The process label must be
unconfined, the selected profile names must be absent from the loaded list, and unrelated profiles must still appear in enforce mode.complainmode is different from unloading a profile and can still enforce explicit deny rules. - Retry the application operation that AppArmor previously denied.
A previously denied read or write should now work. A continuing failure can come from ordinary permissions, another profile, or another security mechanism; disabling more profiles is not proof of a fix.
- Reboot the system to test the disabled profile's startup state.
$ sudo reboot
- Restore the application's example values in the new login shell.
profile=/etc/apparmor.d/usr.local.bin.report-reader
service=report-reader
- Confirm that the application remains unconfined after reboot.
$ sudo cat "/proc/$(systemctl show --property MainPID --value "$service")/attr/current"
- Confirm that the disabled profile stays absent after reboot.
$ sudo aa-status
The same target-absent, process-unconfined, and other-profiles-enforcing checks must still hold.
- Retry the application operation that AppArmor previously denied after the reboot.
The previously denied read or write should now work after the application restarts.
Steps to re-enable one AppArmor profile:
- Remove the disable link for the affected profile.
$ sudo rm /etc/apparmor.d/disable/usr.local.bin.report-reader
The filename must match the profile disabled earlier. If
aa-enforceis installed,sudo aa-enforce “$profile”replaces removing the link and reloading the profile. - Reload the profile into the kernel.
$ sudo apparmor_parser -r "$profile"
A process started while unconfined remains unconfined when this profile is loaded again. Reloading policy alone does not restore confinement to that running process.
- Restart the application under its restored profile.
$ sudo systemctl restart "$service"
- Confirm that the restarted application is confined again.
$ sudo cat "/proc/$(systemctl show --property MainPID --value "$service")/attr/current"
- Check the target and unrelated profiles in the loaded list.
$ sudo aa-status
The process should show its profile with
(enforce), and the profile should be back in the enforced list. - Retry the application operation explicitly denied by the restored profile.
The read or write should fail again with a permission-denied error.
Steps to re-enable AppArmor system-wide:
- Remove the dedicated GRUB drop-in created earlier.
$ sudo rm /etc/default/grub.d/99-disable-apparmor.cfg
If
apparmor=0was added to an existing file instead, remove only that argument with your editor and preserve the other settings. - Regenerate the GRUB configuration without the disabling argument.
$ sudo update-grub
- Enable the AppArmor profile-loading service if it was disabled.
$ sudo systemctl enable apparmor
- Reboot the system with AppArmor enabled.
$ sudo reboot
- Check that AppArmor is enabled after the reboot.
$ aa-enabled
- Check that the kernel's AppArmor parameter is enabled.
$ cat /sys/module/apparmor/parameters/enabled
- Confirm restored confinement after the reboot.
$ sudo aa-status
Expect
Yes,Y, and loaded profiles in enforce mode. Profiles still marked in/etc/apparmor.d/disable/remain disabled until their links are removed. - Restore the application's example values in the new login shell.
profile=/etc/apparmor.d/usr.local.bin.report-reader
service=report-reader
- Confirm that the running application has its enforced profile after the reboot.
$ sudo cat "/proc/$(systemctl show --property MainPID --value "$service")/attr/current"
/usr/local/bin/report-reader (enforce)
- Retry the application operation explicitly denied by the restored profile.
The read or write should fail again with a permission-denied error.
Recovery when the system does not boot
If a GRUB edit prevents booting, open the GRUB menu through the machine's console. Select the normal boot entry, press e, remove apparmor=0 from the line beginning with linux, and press Ctrl+x to boot that temporary edit. After login, remove the persistent argument and run sudo update-grub before another reboot. If the menu is hidden, the firmware or provider's console instructions determine how to reveal it. No network session can repair a machine that has not booted.