A broken SSH server configuration can block new logins. Run sshd -t to check SSH server configuration syntax and host keys before applying a change.
The OpenSSH daemon reads /etc/ssh/sshd_config by default and any files matched by an Include directive, commonly /etc/ssh/sshd_config.d/*.conf on Linux packages. Its test mode parses that configuration tree and checks host keys without starting or reloading the daemon.
With no reported problems, the test returns no output and exits with status 0; a fatal error prints diagnostics and exits with a nonzero status. This validates the files on disk, not the settings already loaded by the running service, and it does not prove that authentication or network access will work.
Steps to test SSH server configuration:
- Run the sshd test mode on the server's configuration.
$ sudo sshd -t
No output means the configuration passed. sudo supplies the privileges needed to read private host keys. To test a complete copy of the main file before installing it, add -f and its path, as in sudo sshd -t -f /root/test_sshd_config.
- Correct the file and line named in any error.
$ sudo sshd -t
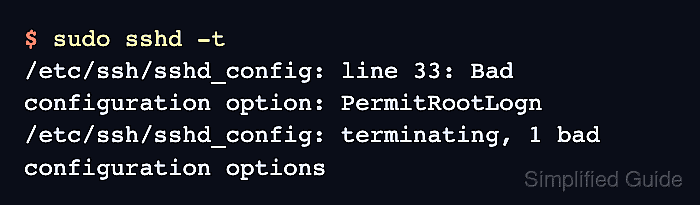
/etc/ssh/sshd_config: line 33: Bad configuration option: PermitRootLogn
/etc/ssh/sshd_config: terminating, 1 bad configuration options
Bad configuration option means the server does not recognize the keyword, usually a misspelling, an option the installed OpenSSH version does not support, or a client option placed in a server file. The named file can also be a drop-in under /etc/ssh/sshd_config.d. A host-key error instead points to the key files or their permissions.
- Run the test again to confirm that it prints nothing.
$ sudo sshd -t
A passing test does not check who is allowed to log in, so a reload can still block new logins. If you apply the change, keep your current session open until a fresh login succeeds.
Related: How to manage the SSH server service with systemctl
Related: How to log in to an SSH server from Linux
Related: How to enable verbose SSH server logging