An SSH server sometimes needs an additional listening port in Linux for a migration, firewall exception, or management network. The existing port stays available alongside the new one, so clients can continue using the original connection details.
OpenSSH supports multiple Port directives in sshd_config, and sshd listens on each one. On Ubuntu 24.04 and later, systemd holds the listening sockets through ssh.socket and reads those directives when it reloads, so the socket is what gets restarted. Both ports use the same host keys and user accounts.
Every new listener must fit the surrounding network policy. A host firewall, cloud rule, or SELinux policy can block an otherwise valid alternate port. An installed OpenSSH server managed by systemd is the starting point, and the job is finished when a new login works on each port.
Steps to make an SSH server listen on multiple ports in Linux:
- Keep a known-good SSH session or console open until both ports accept new logins.
A failed listener change can lock out remote administrators, and the open session is the way to undo it.
- List the TCP ports the server is already listening on.
$ ss -tln
State  Recv-Q Send-Q Local Address:Port Peer Address:Port
LISTEN 0      4096         0.0.0.0:22        0.0.0.0:*
LISTEN 0      4096   127.0.0.53%lo:53        0.0.0.0:*
LISTEN 0      4096      127.0.0.54:53        0.0.0.0:*
LISTEN 0      4096            [::]:22           [::]:*
The examples keep 22 and add 2222. A server on a different port uses that port in place of 22, and the added port must not already be in this list.
- Back up the SSH server configuration.
$ sudo cp /etc/ssh/sshd_config /etc/ssh/sshd_config.bak
If a later restart fails, copying this file back from the open session restores the old settings.
- Open the SSH server configuration in an editor.
$ sudoedit /etc/ssh/sshd_config
- Add one Port line for each listener before any Match block.
Port 22
Port 2222
Both lines are needed because adding any Port line replaces the default of 22. A commented #Port 22 line has no effect.
- Test the sshd configuration.
$ sudo sshd -t
No output means sshd parsed the configuration and host keys successfully.
Related: How to test SSH server configuration - Allow the added TCP port through the firewall from the networks that need it.
An allow rule with no source limit exposes SSH on the new port to every reachable client.
A cloud security group, network ACL, or NAT rule in front of the server needs the same change for 2222/tcp. On systems that use SELinux, such as RHEL and Fedora, also run sudo semanage port -a -t ssh_port_t -p tcp 2222, which comes from policycoreutils-python-utils.
Related: Allow a port through the firewall in Linux - Reload systemd so Ubuntu picks up the new ports.
$ sudo systemctl daemon-reload
Ubuntu 24.04 and later set the ssh.socket ports from the Port lines during this reload. Other distributions do not need it, and it does no harm there.
- Restart SSH to open the added port.
$ sudo systemctl restart ssh.socket
Where ssh.socket is not in use, such as on Debian, use sudo systemctl restart ssh. On RHEL-family systems, use sudo systemctl restart sshd.
Related: How to manage the SSH server service with systemctl - Check that both ports are now listening.
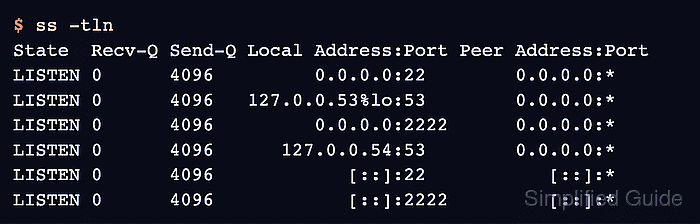
$ ss -tln
State  Recv-Q Send-Q Local Address:Port Peer Address:Port
LISTEN 0      4096         0.0.0.0:22        0.0.0.0:*
LISTEN 0      4096   127.0.0.53%lo:53        0.0.0.0:*
LISTEN 0      4096         0.0.0.0:2222      0.0.0.0:*
LISTEN 0      4096      127.0.0.54:53        0.0.0.0:*
LISTEN 0      4096            [::]:22           [::]:*
LISTEN 0      4096            [::]:2222         [::]:*
If Ubuntu still shows only the original port, a local override under /etc/systemd/system/ssh.socket.d/ is setting the ports.
Related: How to make SSH listen on a specific IP address in Linux - Test a new login through the original port from another computer.
$ ssh -p 22 user@host.example.net whoami
user
The hostname and username stand for your server and account.
Related: How to connect to an SSH server on a different port - Test a new login through the additional port.
$ ssh -p 2222 user@host.example.net whoami
user
A first login on the new port can ask you to accept the host key, which is the same key the server uses on the original port. If this login times out, check the firewall, cloud security group, or NAT rule for port 2222/tcp.