Crashes, stalled services, and driver problems often leave records in Windows even after a restart. The System log in Event Viewer lets you check what Windows components reported around the time a problem occurred.
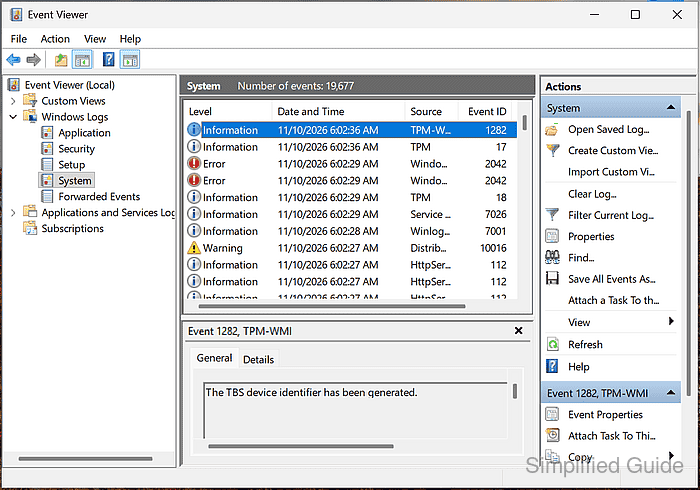
Windows Logs separates System events from application failures and security audit records. Each system event has a timestamp, a source, an event ID, and a severity level, with a description explaining what the component reported.
An Error or Warning is a clue rather than proof that an event caused the symptom. The time and description need to fit what happened, and older records may already have been overwritten when the log reached its size limit.
Steps to view system logs on Windows:
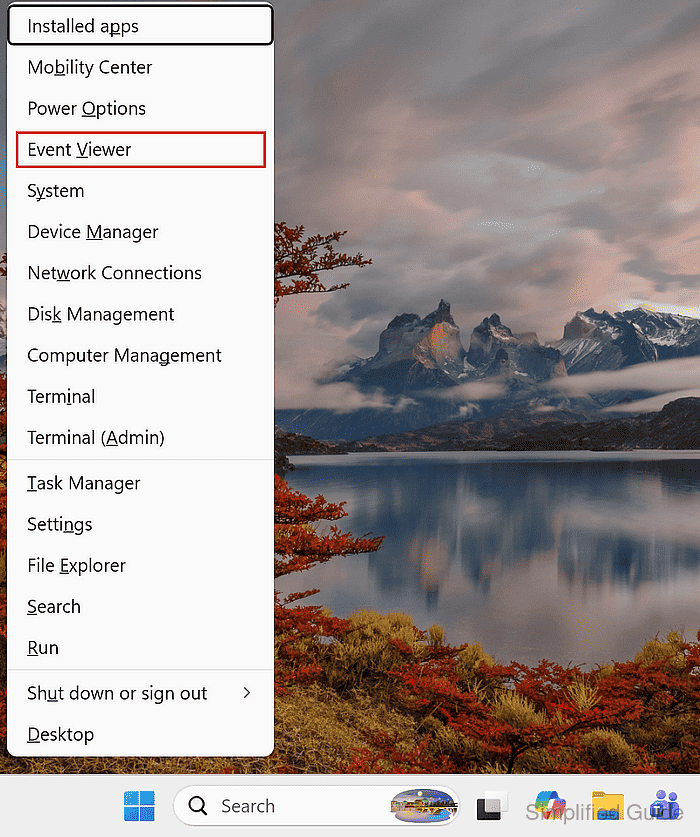
- Press Windows + X to open the menu beside Start.
- Select Event Viewer from the menu.
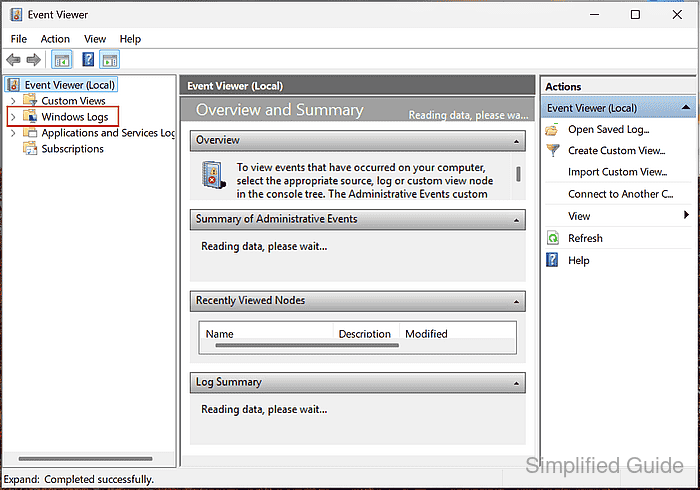
- Expand Windows Logs in the left pane.
- Select System under Windows Logs.
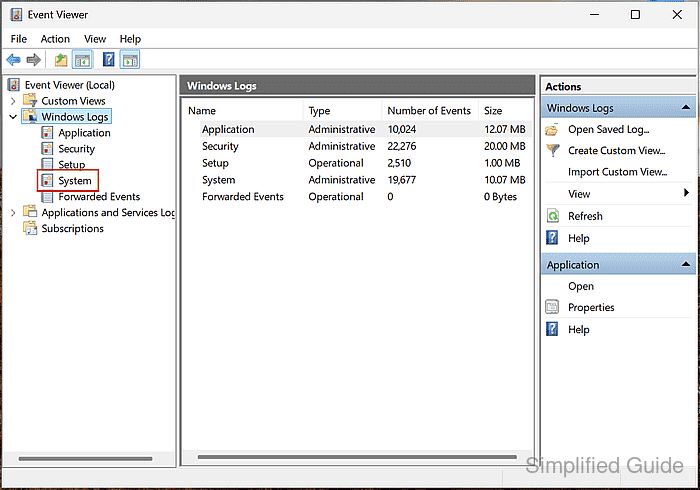
System contains events from Windows components, including drivers and services. Application contains application events, while Security contains audit records.
- Double-click an event with a Date and Time near the problem.
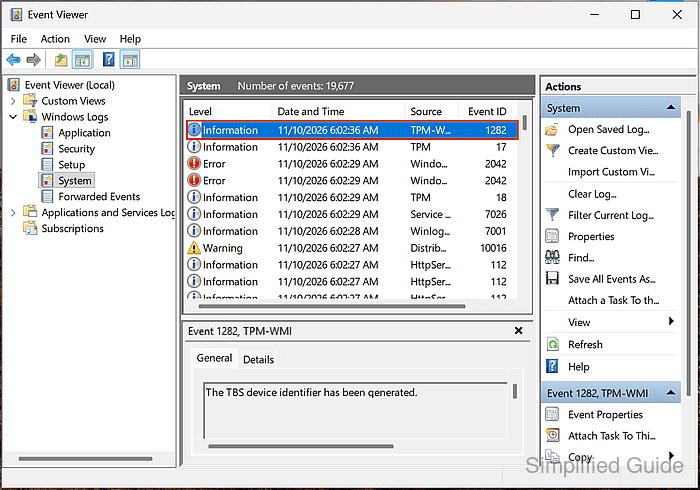
The event list can be scrolled to earlier times. Information entries can help establish the sequence of events alongside Critical, Error, and Warning entries.
- Read the description and the Logged, Source, Event ID, and Level fields on the General tab.
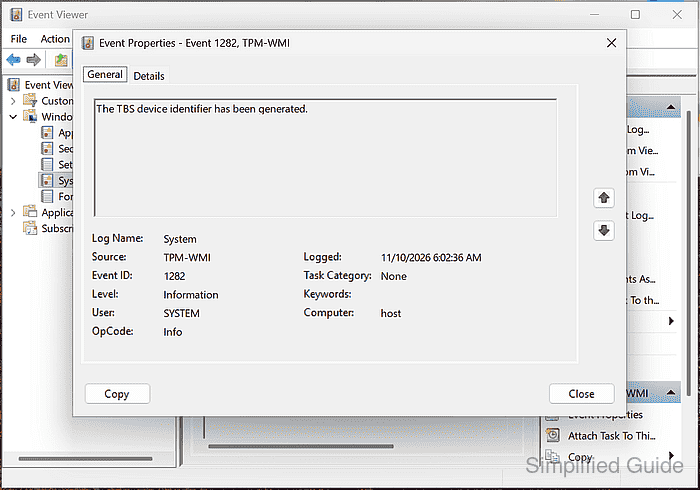
Log Name should be System. The source and event ID identify the event together, while Logged gives its time. The Information event shown reports that a device identifier was generated; it does not report a failure.