Proxy settings in a Linux terminal depend on the destination protocol. Exporting https_proxy selects a temporary proxy route for HTTPS requests from compatible commands started in that shell, and a request check confirms that traffic passes through the chosen proxy.
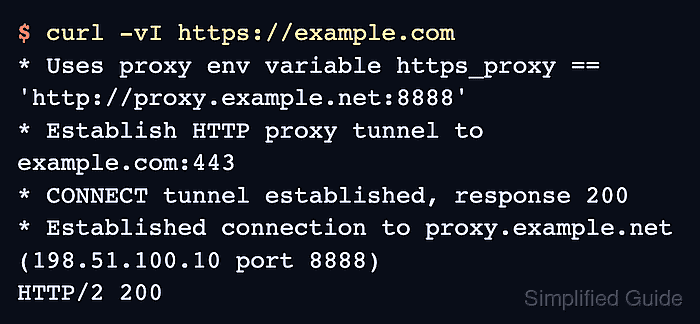
For an HTTPS destination, clients such as curl and wget read https_proxy to find the proxy endpoint. The proxy URL often still starts with http:// because the client speaks HTTP to the proxy first, asks for a CONNECT tunnel to the remote HTTPS server, and then runs TLS through that tunnel.
With a session-scoped export, a curl request shows the route through the proxy before other commands use it. Keep proxy credentials out of reusable shell history, use no_proxy only for approved direct destinations, and move the same exports to the Bash or Zsh startup guides only when future terminals should inherit the proxy automatically.
Steps to use a proxy for HTTPS requests in Linux:
- Export the HTTPS proxy for commands started from this shell.
$ export https_proxy="http://proxy.example.net:8888"
A normal HTTP proxy takes an http:// URL like this one. An https:// proxy URL applies only when the proxy listener itself expects TLS from clients.
If proxy authentication is required, avoid placing reusable passwords in shell history, shared scripts, or startup files unless that exposure is allowed.
- Export a bypass list only for destinations that should stay direct.
$ export no_proxy="localhost,127.0.0.1,.example.internal"
Entries are comma-separated. A leading dot commonly matches a domain suffix, but exact no_proxy matching still depends on the client.
- Check an HTTPS request through the proxy with curl.
$ curl -vI https://example.com
* Uses proxy env variable no_proxy == 'localhost,127.0.0.1,.example.internal'
* Uses proxy env variable https_proxy == 'http://proxy.example.net:8888'
* Establish HTTP proxy tunnel to example.com:443
> CONNECT example.com:443 HTTP/1.1
< HTTP/1.1 200 Connection established
##### snipped #####
* CONNECT tunnel established, response 200
##### snipped #####
* Established connection to proxy.example.net (198.51.100.10 port 8888) from 198.51.100.20 port 44446
* using HTTP/2
##### snipped #####
< HTTP/2 200
HTTP/2 200
##### snipped #####
The https_proxy value, the CONNECT request, and the connection to the proxy host show that the request went through the proxy.
Related: Use proxy environment variables with cURL
Tool: Proxy Server CheckerA client that still connects directly may ignore shell proxy variables, use its own config file, or match no_proxy.
Related: Use an HTTP proxy with wget - Remove the session-scoped proxy variables when direct access should resume.
$ unset https_proxy no_proxy
Clear uppercase variants such as HTTPS_PROXY and NO_PROXY as well when an older shell or application still inherits them.
Related: How to unset an environment variable in Linux