Apache uses its worker identity to access site files. On Ubuntu or Debian, a dedicated user and group can keep content read-only while allowing specific data writes; permission checks and a site request confirm the change works.
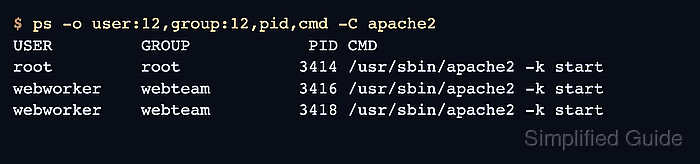
On Unix-family systems, Apache starts with enough privilege to bind its listening ports, then request-handling child processes switch to the configured User and Group. A root parent process in the process list is expected after a successful change; the child processes are the lines that must show the new account and group.
The Ubuntu and Debian apache2 packages normally use www-data for request handling. Their environment file supplies the account names for the server-wide User and Group directives, so a change affects every site served by that Apache instance. It does not assign a separate identity to one virtual host with AssignUserID or change a separate PHP-FPM process's account.
Steps to change Apache user and group on Ubuntu and Debian:
- Create the dedicated service group.
$ sudo groupadd --system webteam
- Create the service account in that group.
$ sudo adduser --system --ingroup webteam webworker
Do not use root or a personal login account for request handling.
- Back up the Apache environment file.
$ sudo cp /etc/apache2/envvars /etc/apache2/envvars.bak
The new identity applies to every site on this Apache server. A wrong account name or missing file access can take them all offline after the restart, and the restart itself interrupts active requests.
- Open the Apache environment file in your editor.
$ sudoedit /etc/apache2/envvars
- Set APACHE_RUN_USER and APACHE_RUN_GROUP to the new identity.
- /etc/apache2/envvars
export APACHE_RUN_USER=webworker
export APACHE_RUN_GROUP=webteam
Both lines normally name www-data. The rest of /etc/apache2/envvars stays intact.
- Check that the new account can read your site's files.
$ sudo -u webworker head -n 1 /srv/www/www.example.net/index.html
Apache site is responding.
The path and the returned text will be your site's. Permission denied means the account cannot reach that file or a folder above it, and a restart will not fix that. A file ACL can give the webteam group read access without changing the existing permissions.
- Give the new account ownership of any folder the site writes to, such as uploads.
A recursive chown on the whole site lets Apache rewrite its own pages, and one on a shared path such as /var can break other software.
$ sudo chown -R webworker:webteam /srv/www/www.example.net/uploads
- Test the Apache configuration before restarting the service.
$ sudo apache2ctl configtest
Syntax OK
A warning such as AH00558: Could not reliably determine the server's fully qualified domain name does not usually block the restart when the final line is Syntax OK.
- Restart the Apache service to apply the new identity.
$ sudo systemctl restart apache2
If the restart or the site check fails, the backup returns Apache to the old account.
$ sudo cp /etc/apache2/envvars.bak /etc/apache2/envvars
$ sudo systemctl restart apache2
A folder moved to the new account also needs its old owner back, usually with sudo chown -R www-data:www-data.
- Verify the identity of the running Apache child processes.
$ ps -o user:12,group:12,pid,cmd -C apache2
USER         GROUP            PID CMD
root         root             369 /usr/sbin/apache2 -k start
webworker    webteam          371 /usr/sbin/apache2 -k start
webworker    webteam          372 /usr/sbin/apache2 -k start
The root line is the parent process. The request-handling child processes should show the replacement User and Group values.
- Open the site to confirm it still loads.
$ curl http://www.example.net/
Apache site is responding.
The address and page content will be your site's, and a browser shows the same result. A test upload confirms any folder you moved to the new account.